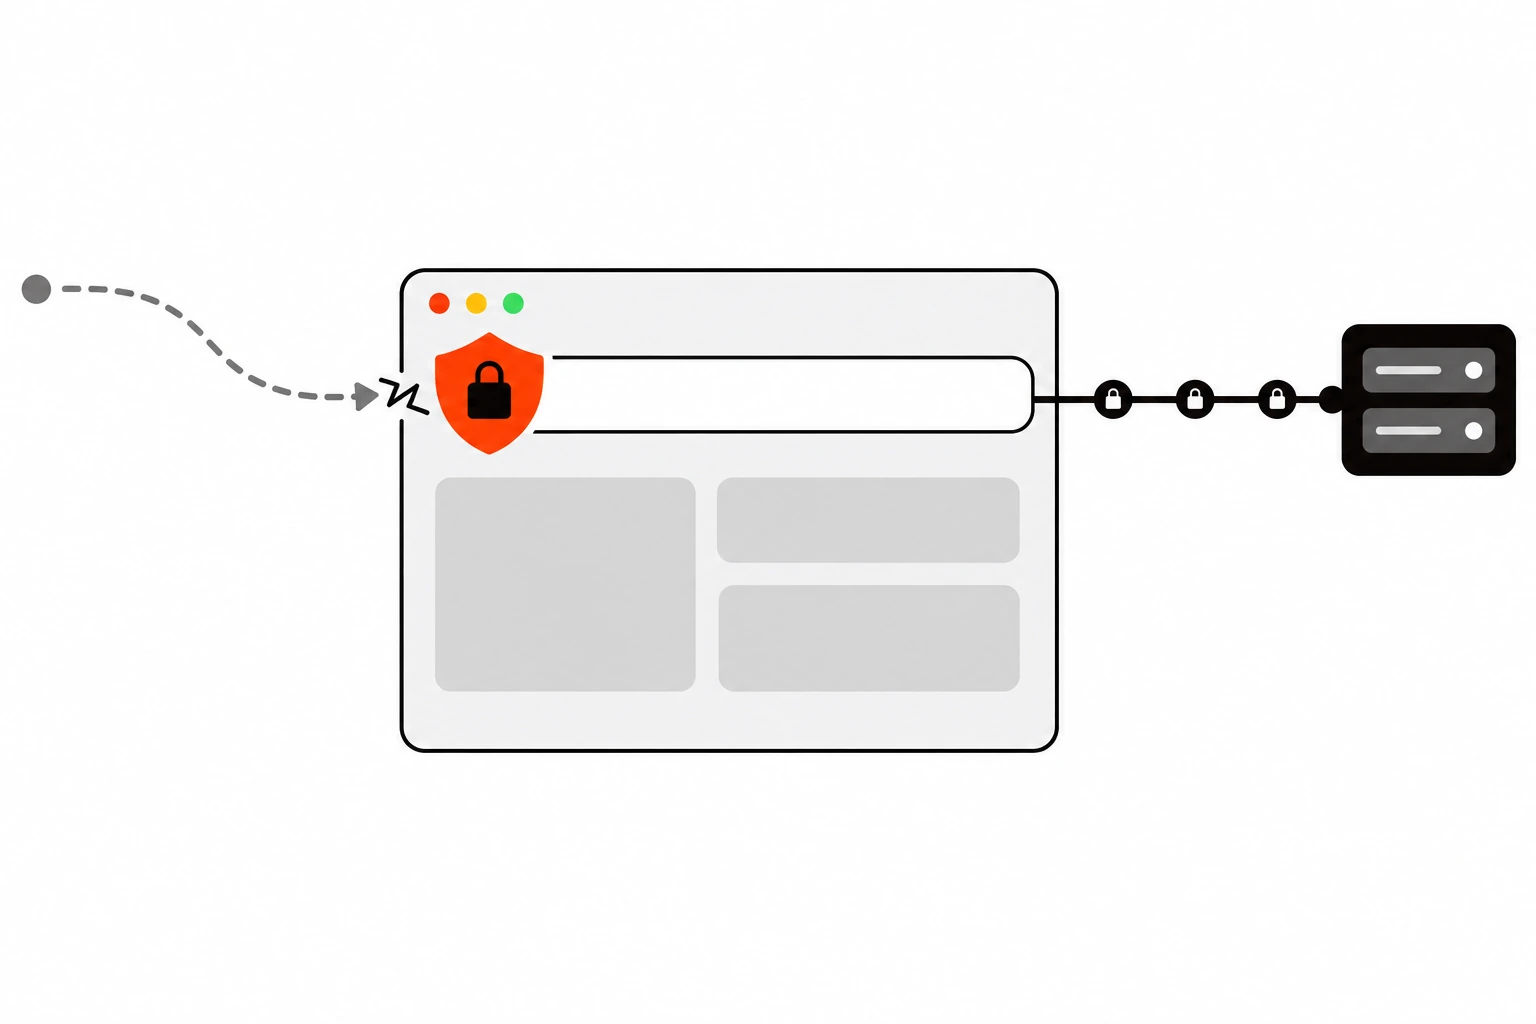
HSTS Explained: How Strict-Transport-Security Closes the HTTPS Downgrade Gap
A 301 redirect to HTTPS still lets the first plain HTTP request out. Here’s how HSTS closes that gap: the Strict-Transport-Security header and its directives, a safe max-age ramp, what breaks, the preload list and its requirements, setup in Nginx, Apache, Next.js, Vercel, Cloudflare and WordPress hosts, checking it with curl, and clearing it in Chrome.
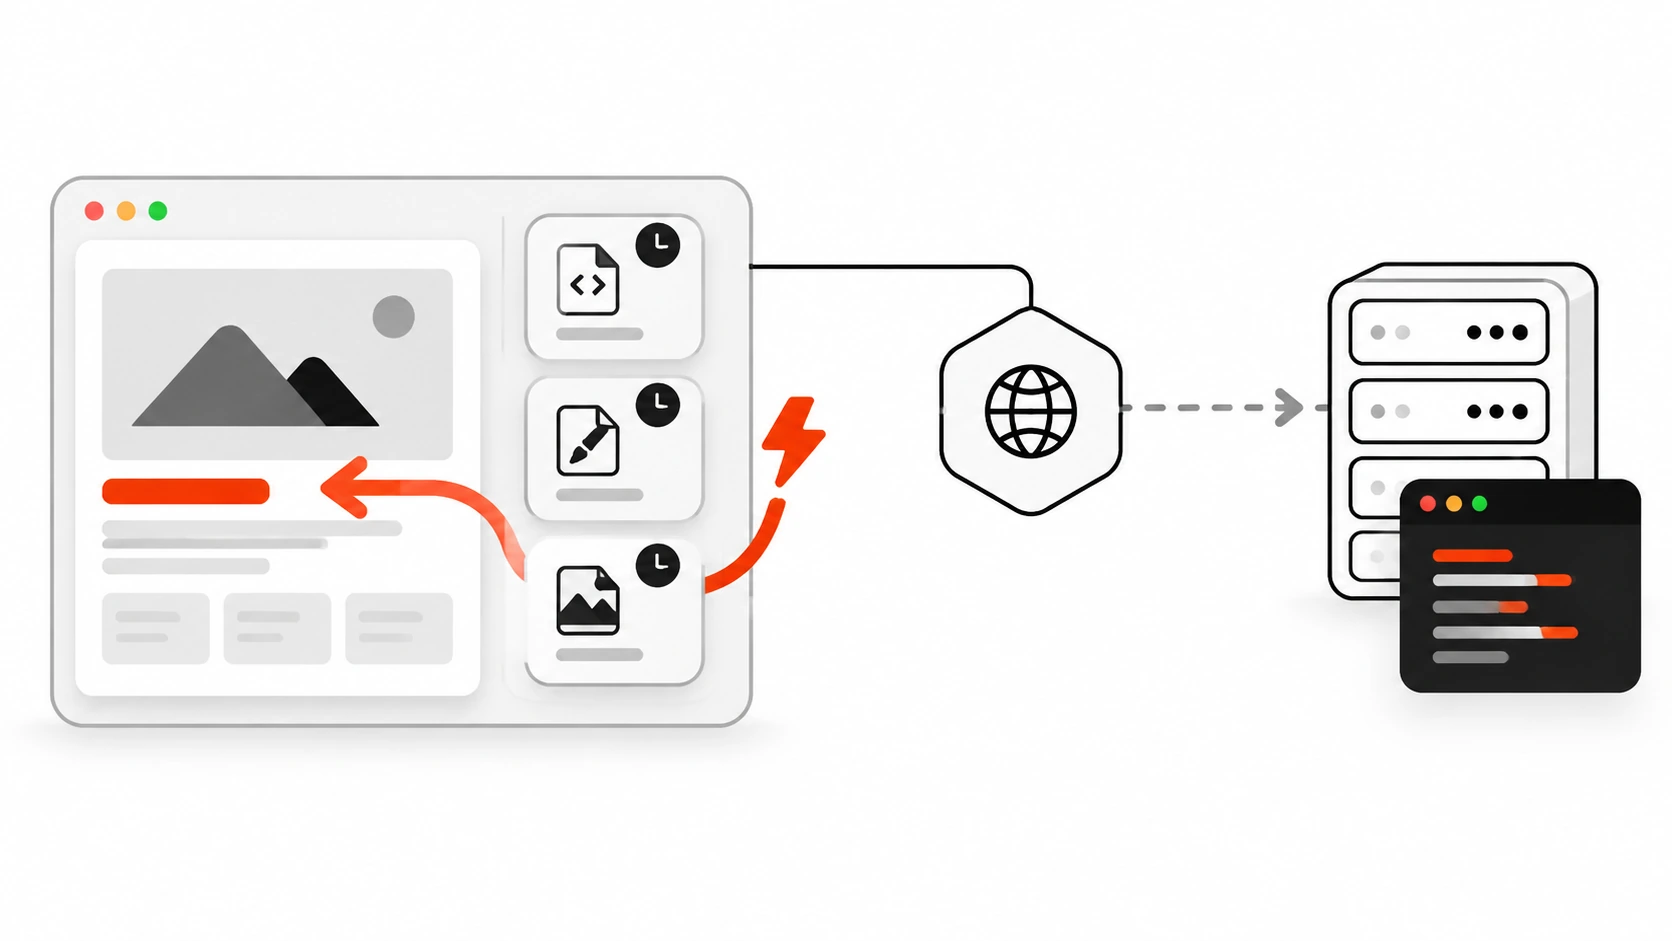
Cache-Control Headers in 2026: Caching Rules That Make Repeat Visits Instant
How I set Cache-Control headers on client sites: hashed assets cached for a year, HTML revalidated with ETags, private pages kept out of shared caches, and CDN rules that just work.