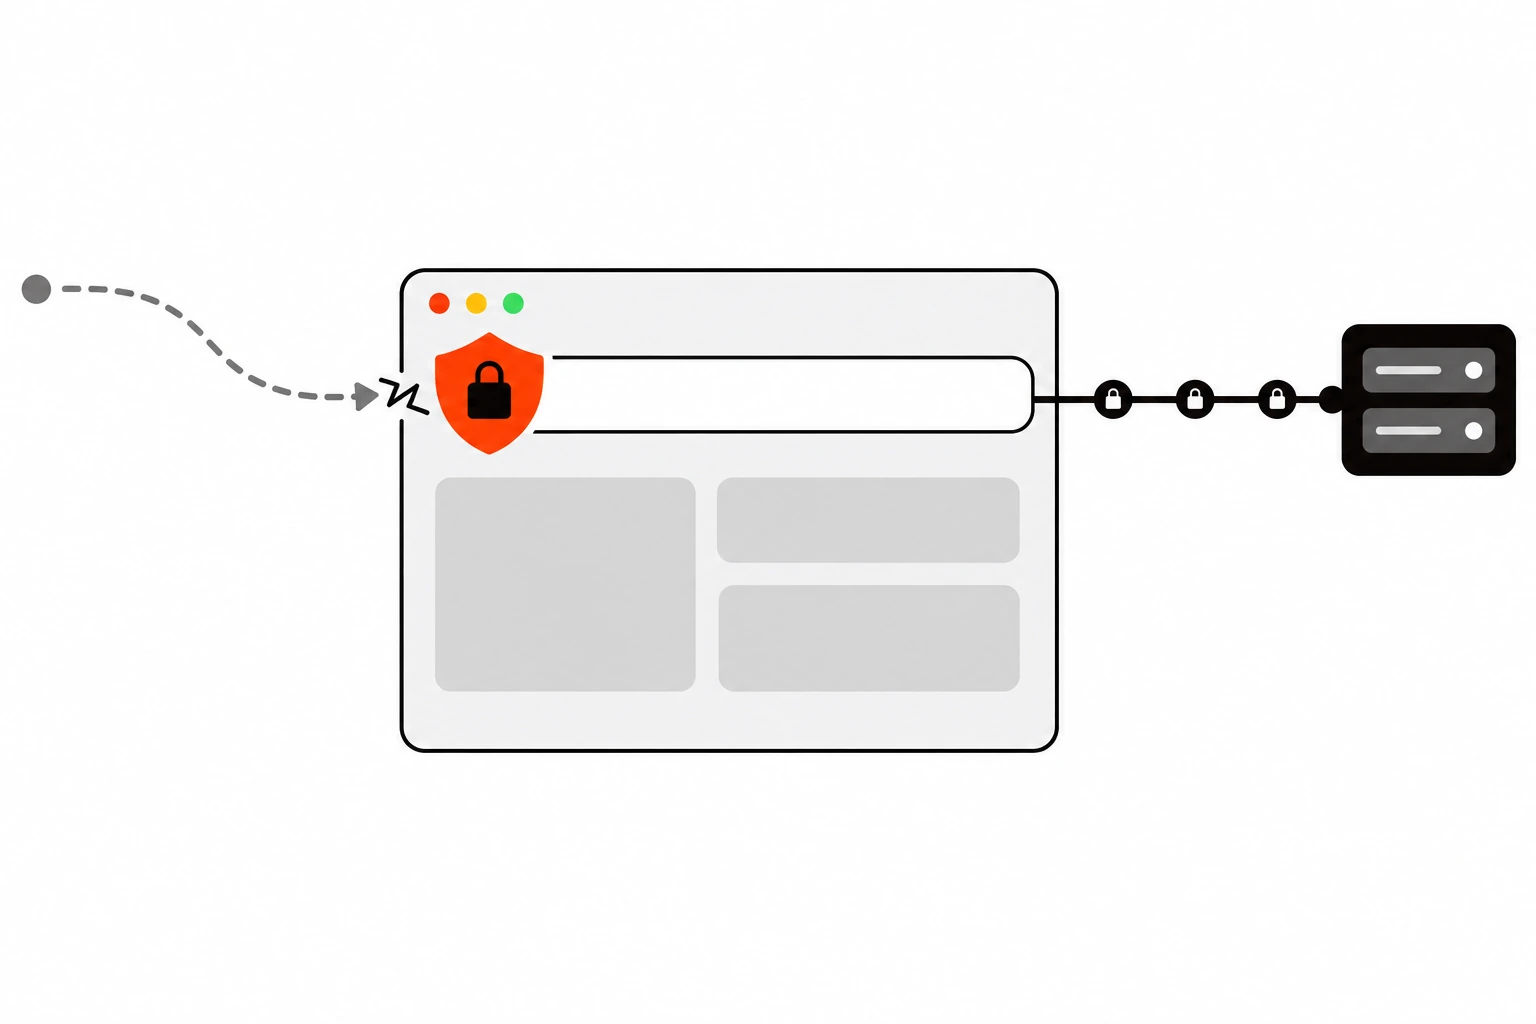
HSTS Explained: How Strict-Transport-Security Closes the HTTPS Downgrade Gap
A 301 redirect to HTTPS still lets the first plain HTTP request out. Here’s how HSTS closes that gap: the Strict-Transport-Security header and its directives, a safe max-age ramp, what breaks, the preload list and its requirements, setup in Nginx, Apache, Next.js, Vercel, Cloudflare and WordPress hosts, checking it with curl, and clearing it in Chrome.
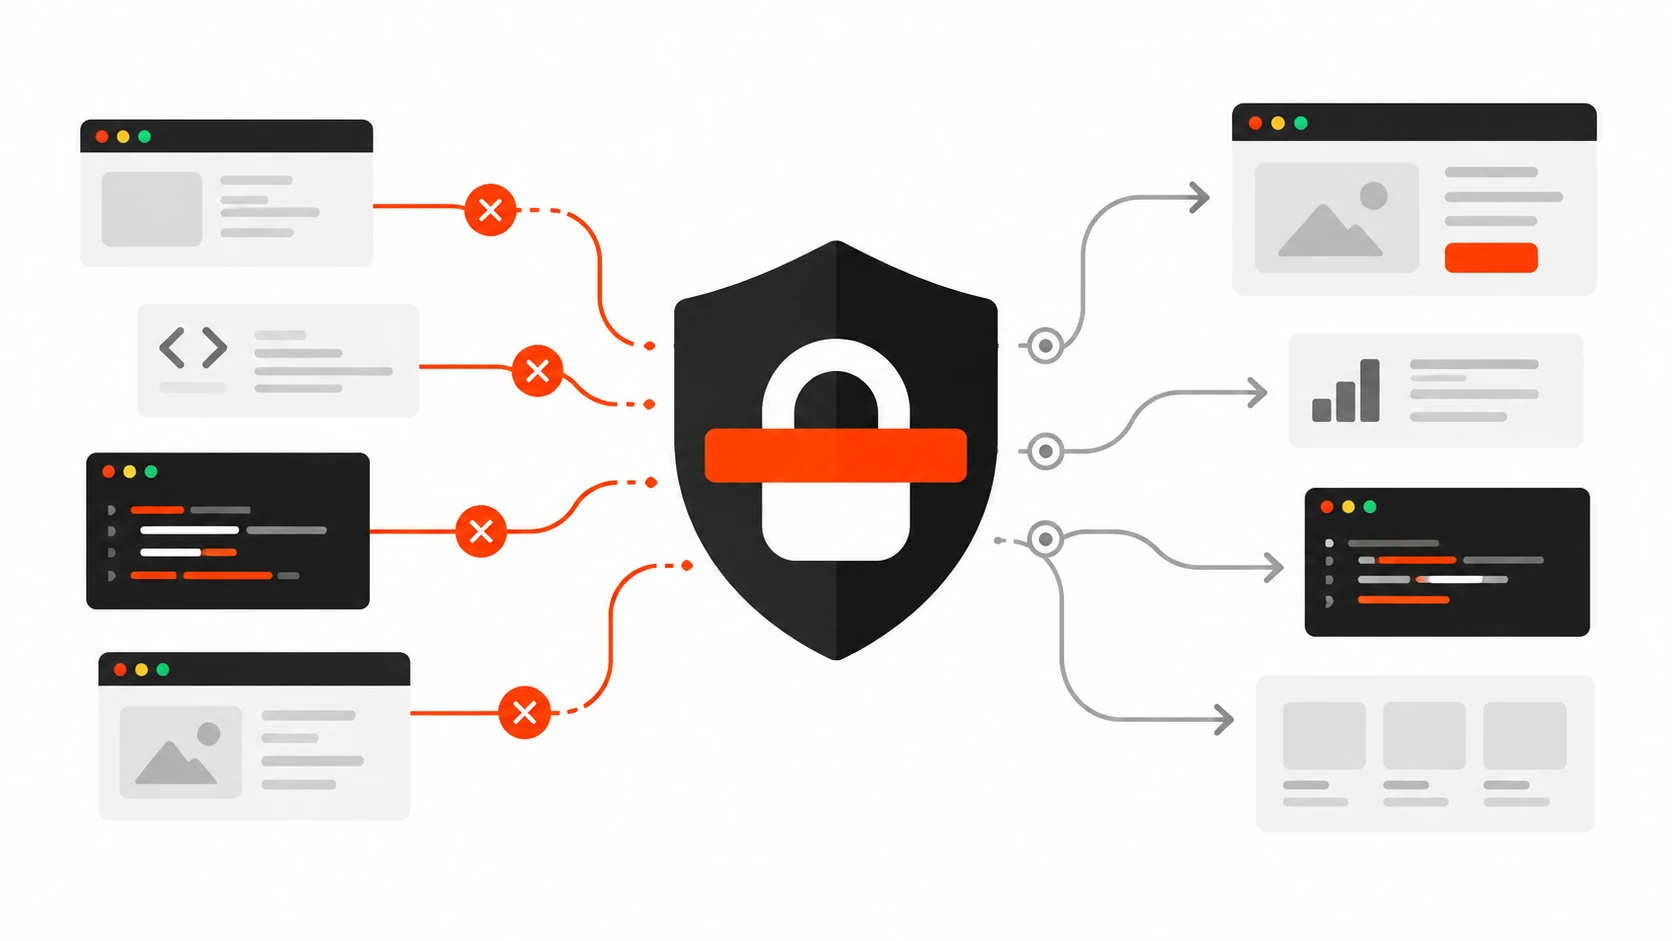
Content Security Policy in 2026: Lock Down XSS Without Breaking Your Scripts
Practical CSP in 2026: report-only rollout, nonces vs hashes vs strict-dynamic, WordPress and Next.js headers, GTM, and a checklist to stop XSS without breaking scripts.