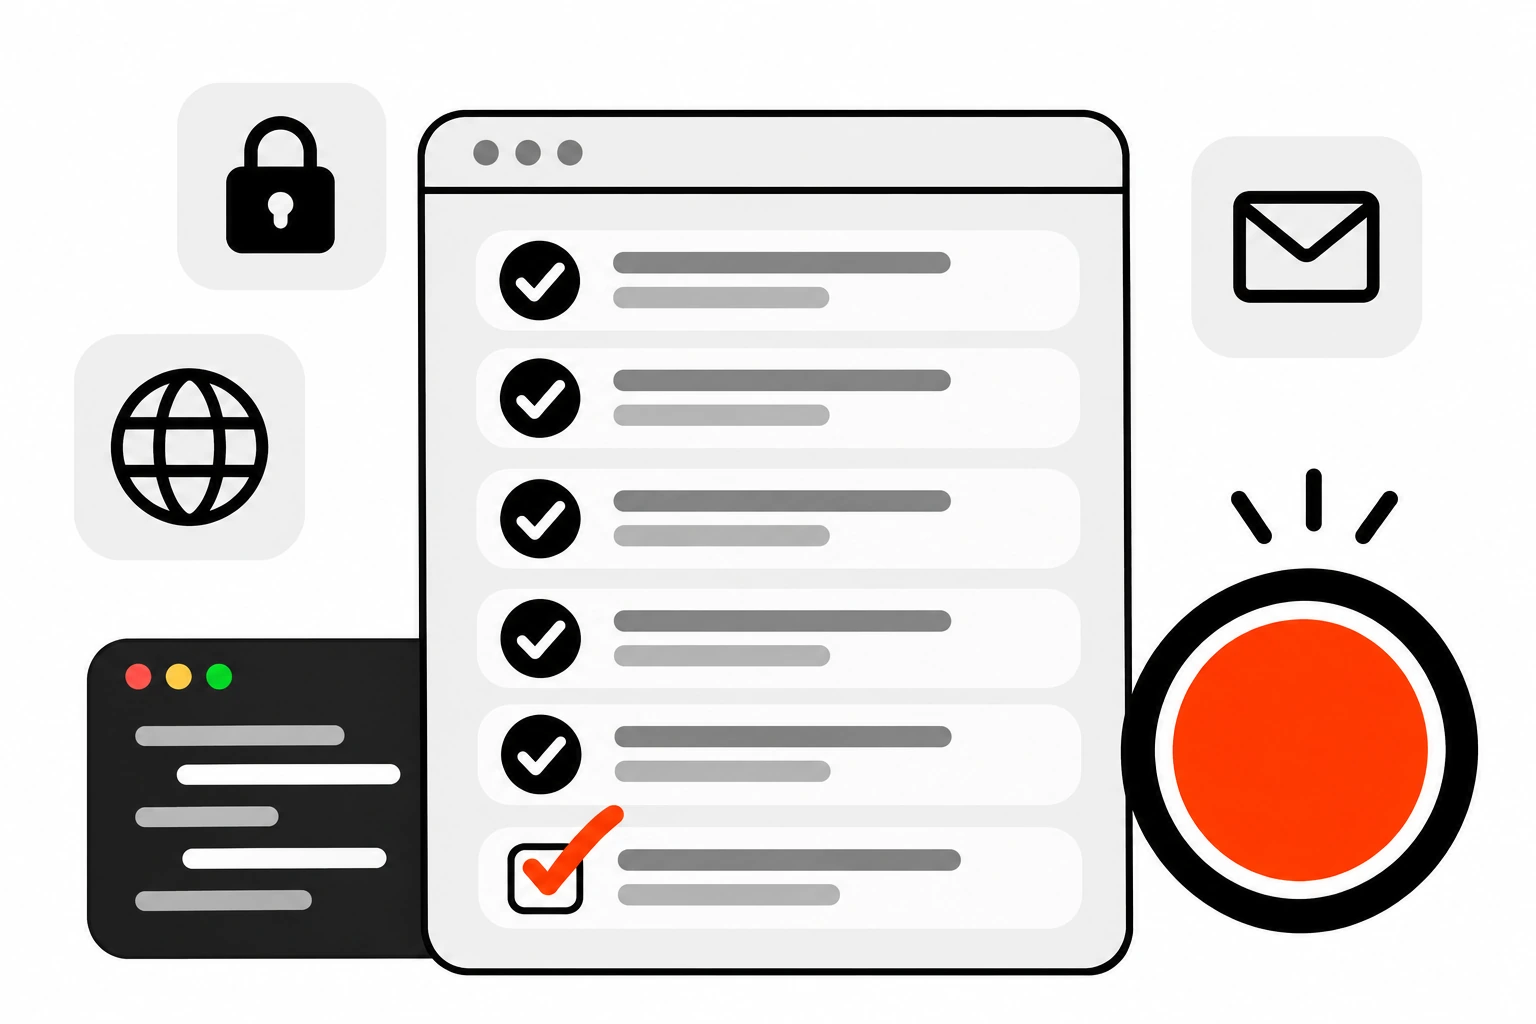
Website Launch Checklist: What to Check Before a Client Site Goes Live
The website launch checklist I run before a client site goes live: the WordPress noindex setting, robots.txt and sitemaps, 301 redirects, HTTPS and HSTS, form email with SPF, DKIM and DMARC, analytics, Core Web Vitals, DNS TTL, backups, cleanup and the client handoff doc.
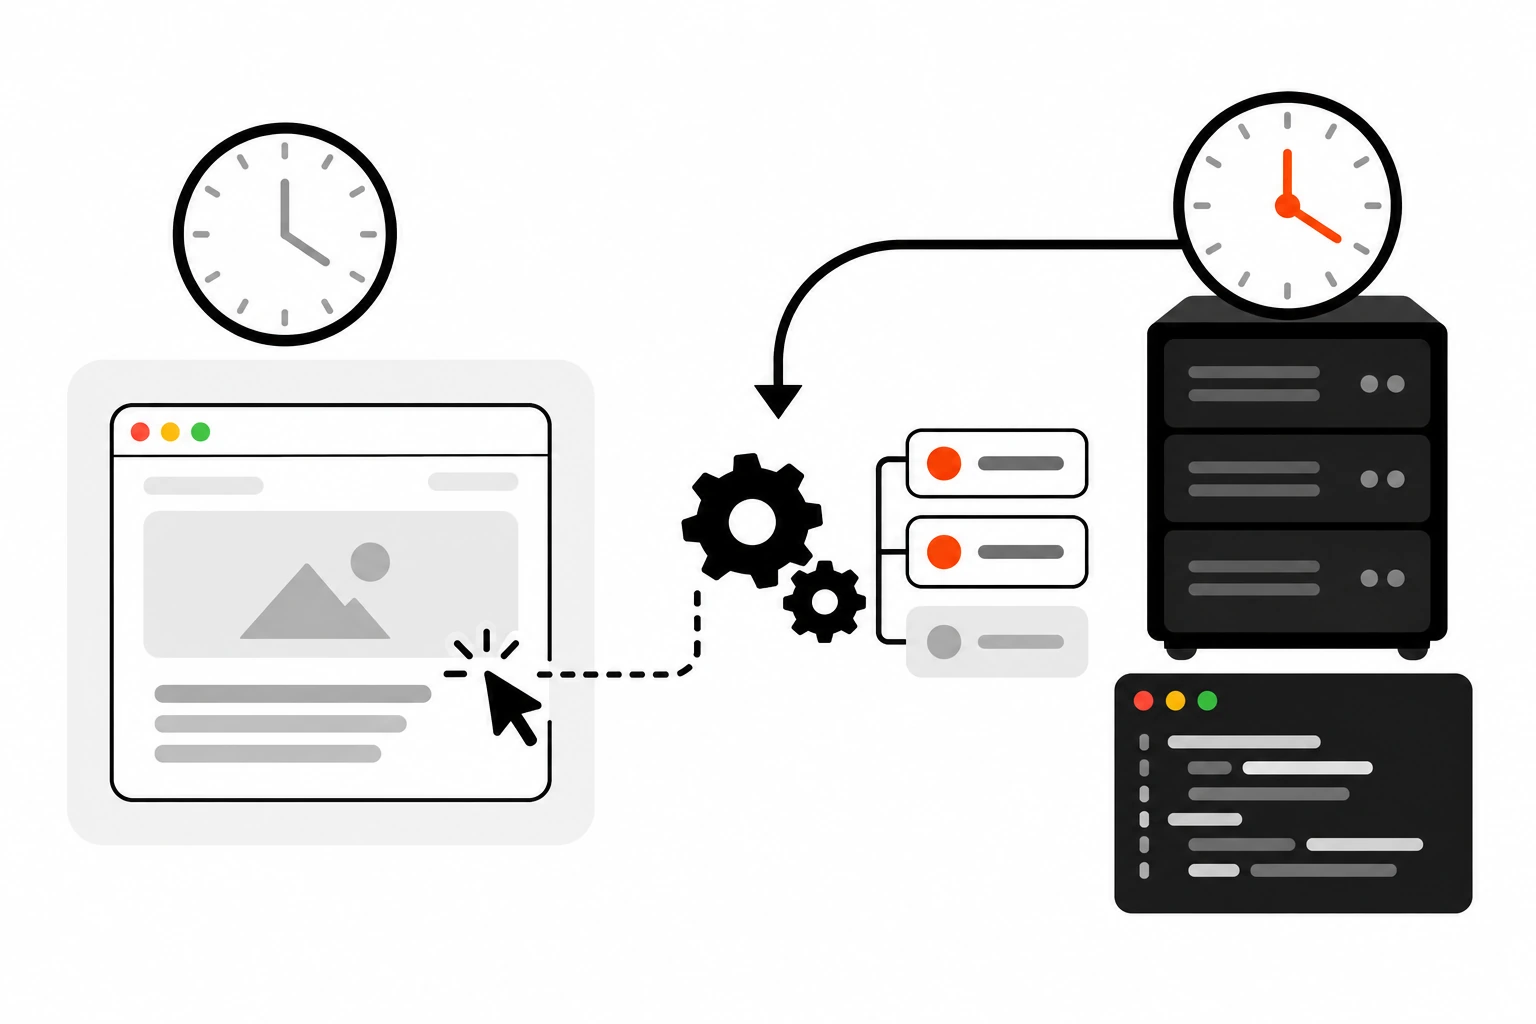
WP-Cron: Why Scheduled Tasks Run Late and How to Use a Real Cron Job
WP-Cron only checks for due tasks when someone loads a page, so quiet or cached sites miss scheduled posts and backups. Here’s how it works, how I switch to a real server cron with DISABLE_WP_CRON and WP-CLI, and how to schedule plugin events without duplicates.
Cache-Control Headers in 2026: Caching Rules That Make Repeat Visits Instant
How I set Cache-Control headers on client sites: hashed assets cached for a year, HTML revalidated with ETags, private pages kept out of shared caches, and CDN rules that just work.
JSON-LD Structured Data in 2026: Schema Markup That Still Earns Rich Results
How I add JSON-LD structured data to client sites in 2026: the schema types that still earn rich results, one connected @graph, safe Next.js and WordPress output, and testing in CI.
Speculation Rules API in 2026: Prerender the Next Page Before the Click
How I use the Speculation Rules API on client sites: prefetch vs prerender, document rules, eagerness levels, safe exclusions, prerender-aware analytics, and WordPress 6.8 speculative loading.
Content Security Policy in 2026: Lock Down XSS Without Breaking Your Scripts
Practical CSP in 2026: report-only rollout, nonces vs hashes vs strict-dynamic, WordPress and Next.js headers, GTM, and a checklist to stop XSS without breaking scripts.